Starting today, Test Replay replaces the values of sensitive form fields (passwords and payment details) with asterisks before it captures the DOM before any Test Replay data is uploaded to Cypress Cloud. It's on by default for every Cypress Cloud project.
This follows the same principle as network data redaction in Test Replay: keep sensitive values out of captured artifacts, without giving up the overall debugging experience of Test Replay in Cypress Cloud. We've heard from Cypress Cloud customers that this collection of changes has already helped them to test more kinds of projects and conform to their internal standards.
This has no effect on test writing or execution, and only relates to the specific process that generates Test Replay artifacts when recording a run to Cypress Cloud.
What gets masked
Cypress masks the values entered into fields that are known to hold sensitive data:
- Password fields (
input[type=password]) - Hidden fields (
input[type="hidden"]) - Credit card and payment fields identified by standard autocomplete attributes
The masked values show as asterisks in the captured DOM. You still get the full form — its structure, layout, and behavior — so a replayed session looks and behaves the way it did during the run. Only the entered values are hidden.
Updating the setting
Masking is on for every project out of the box. If you're an Owner or Admin of your organization, you can turn it off per project under Test Replay in your Cypress Cloud project settings. For everyone else, the setting shows as locked, so the protection can't be switched off by accident.
Here is how this looks in the Cypress Cloud settings:
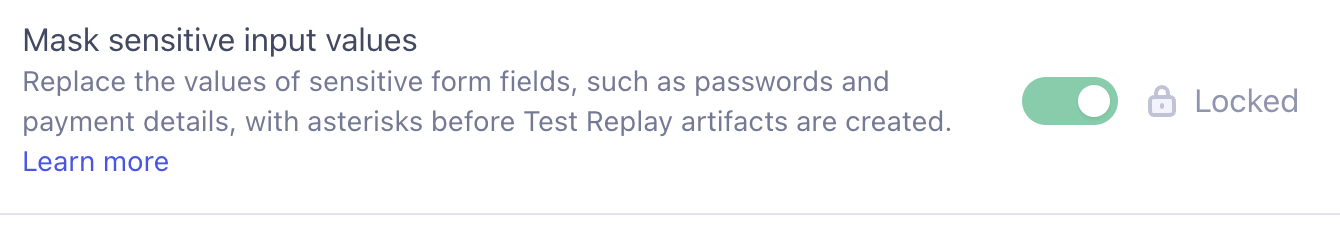
We've made this a setting so that teams who need to see these values in Test Replay have the ability to turn this on.
Why it's useful
Test Replay data is easier to pull down than it used to be. With the Cypress Cloud CLI, you can download and view a Test Replay locally in a couple of commands. While live credentials or credit card info are not expected be in your tests to begin with, if they ever get recorded unintentional, this masking means they aren't sitting in the artifact waiting to be downloaded.
Best practice: Keep sensitive data out of your tests
Masking is a safety net, not a substitute for good test data hygiene. A few practices make a big difference:
- Don't put real sensitive data in recorded tests. Use test credentials and example data with no PII.
- Protect your test credentials and simulated cards. Even fake-looking data can be worth keeping out of shared artifacts. Masking and redaction help here.
- Use
cy.env()to securely load environment variables. - Control what appears in the Command Log. You can hide values from the Cypress Command Log, which controls what appears in screenshots, videos, and Test Replay.
- Control what comes over the wire. Use
cy.intercept()with fixtures to swap image content or any other sensitive response for safe, predictable data — so the real thing never reaches your test or your captured artifacts.
Learn more
For the full list of data controls in Cypress Cloud — network redaction, Command Log masking, screenshot and video controls, and more — see Data storage and controls.
If you spot a sensitive field that should be masked and isn't, let your account team know so we can improve detection.